Audit trail
Document audit trails that keep proof connected
ZaferSign keeps audit evidence connected to the signed record, helping teams review who signed, what changed, when activity happened, and how the document moved through the workflow after completion.
- Signer activity, timestamps, document hashes, and IP context
- Workflow status, process details, and step history
- Certificate report and blockchain-backed evidence
- Validation, retrieval, and completed-record review
Audit timeline
Evidence created as the workflow runs
- 01
Prepare
Fields, recipients, due dates, and workflow controls are defined.
- 02
Route
The document moves through signers, reviewers, carbon copies, and sendbacks.
- 03
Sign
Signer activity, timestamps, and document completion events are captured.
- 04
Verify
Certificate report, validation, and blockchain-backed evidence support review.
- 05
Retrieve
Completed documents and audit context stay available after signing.
Evidence model
Capture more than a completed signature
An audit trail should make the transaction understandable after the signing moment. ZaferSign keeps activity, workflow state, certificate evidence, and retrieval context connected to the completed document.
Signer identity and activity
Capture who acted, assigned users, signer details, completion activity, and signature counts.
Workflow and step history
Preserve process status, step numbers, CC steps, reviewers, sendbacks, and delegation context.
Time and transaction context
Keep created time, modified time, completed time, IP context, and blockchain transaction data connected.
Validation and retrieval
Support later review with validation, certificate report details, completed document access, and downloads.
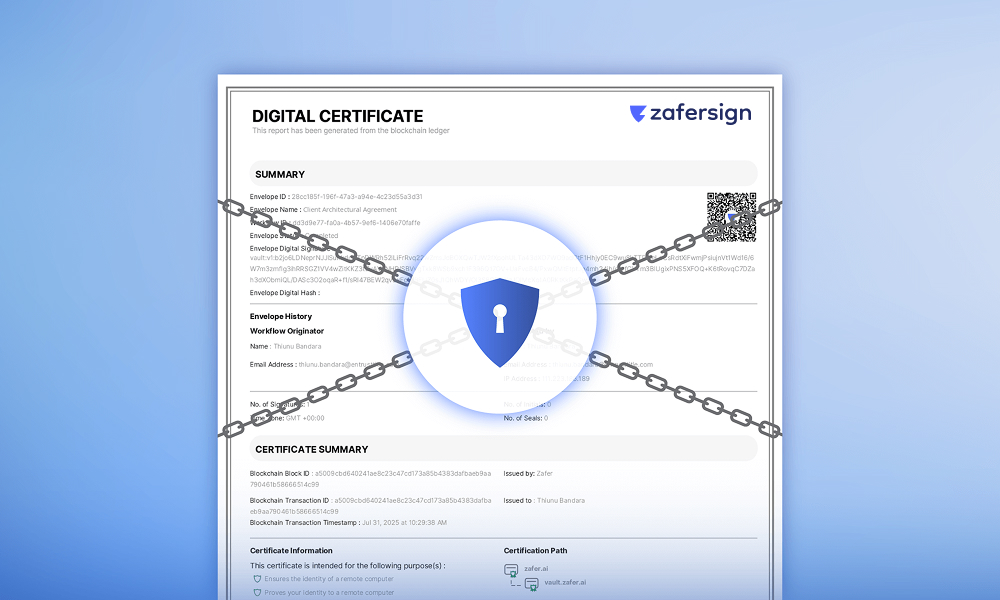
Certificate report
Document evidence, signer details, blockchain transaction data, and audit timestamps remain available after completion.
Certificate report
Keep blockchain-backed document evidence available for review
ZaferSign certificate reports connect the signed record with envelope status, signer details, workflow history, signature counts, blockchain transaction data, and audit timestamps so teams can review the record later.
Audit record fields
Give teams the context needed to answer who, what, and when
Document audit trails are most useful when they combine signer evidence, workflow state, transaction data, validation results, and completed document retrieval in one reviewable record.
Audit record
Everything needed to review the transaction context
Chain of custody
Make the document path easier to defend after completion
When a document matters, teams need to explain who acted, what changed, and when activity happened. ZaferSign keeps that context connected across signing, routing, exceptions, validation, and storage.
Who acted
Creator, assigned users, signers, reviewers, carbon-copy users, and delegated actors.
What happened
Signing, sendback, approval, completion, rejection, expiration, cancellation, and validation events.
When it happened
Created, modified, assigned, completed, and checked timestamps tied to the process.
Evidence API
Retrieve audit context when systems need proof
API and webhooks
Surface audit evidence in connected business systems
Teams can use API endpoints and webhook updates to retrieve process status, standard details, full process details, validation outcomes, process lists, and completed document downloads when audit context needs to move into another system.
Audit-ready document work
Ready to keep document proof connected after signing?
Use ZaferSign to route, sign, validate, store, and retrieve document evidence with audit trails built into the workflow.